
Table of Contents
- • Current edition update — September 2026
- • Understanding the Ten Syllabus Elements
- • Market Risk — What the Exam Tests
- • Credit Risk and Counterparty Exposure
- • Operational Risk — Beyond IT Failures
- • Liquidity Risk and Basel III Requirements
- • Regulatory Frameworks — Basel III and Beyond
- • Building Your Study Plan for the Risk Exam
CISI Risk in Financial Services
Explore syllabus-aligned study tools, realistic practice and course-grounded AI support.
Key Takeaways
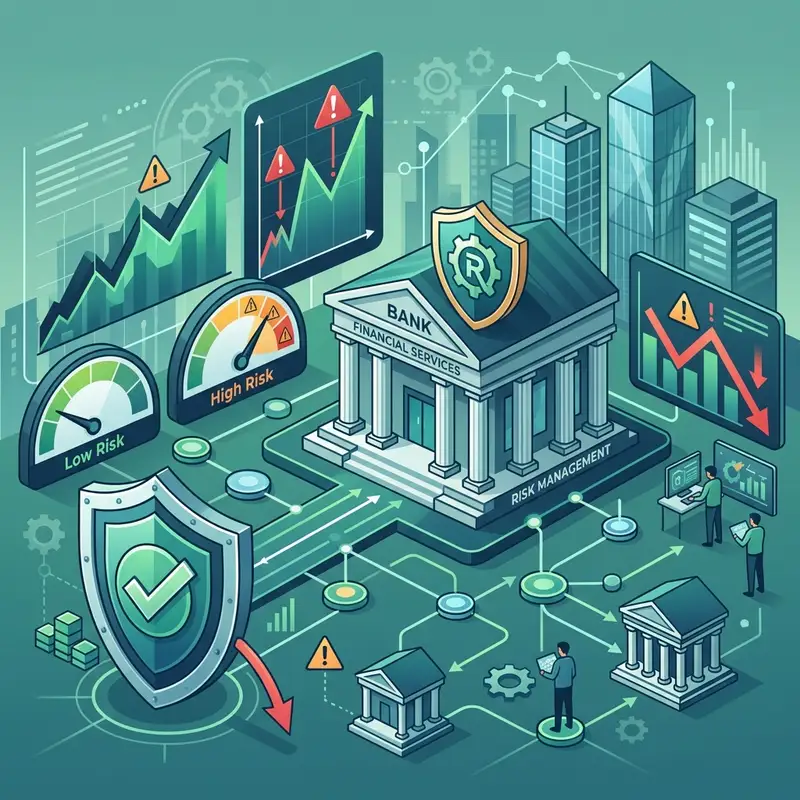
- Scope: Version 12 tests ten weighted elements spanning risk principles, regulation, operational, credit, market, investment, liquidity and model risk, governance and ERM.
- Level: This is a CISI Level 3 Award.
- Strategy: Success depends on understanding how risk categories interact and how regulatory frameworks like Basel III shape real-world risk management.
- Action: Start your preparation today with our interactive CISI Risk in Financial Services course, featuring mock exams, flashcards, and AI-powered tutoring.
The CISI Risk in Financial Services qualification is a Level 3 Award for professionals building knowledge of risk management, compliance, and financial regulation. It tests the ability to identify, measure and manage the risks financial institutions face.
This guide explains the major topics and provides a structured preparation strategy.
Current edition update — September 2026
Version 12 applies from 11 August 2026 to 10 August 2028, with ten-element weights of 13/7/18/16/12/11/8/4/5/6. Our Version 12 preparation was updated on 6 September 2026 against the current syllabus, official sample paper and Candidate Update. It includes 400 unique primary questions, five 100-question mocks, and ten worked calculations, while retaining the official 120-minute format and sample-paper boundary of 70 correct answers.
Understanding the Ten Syllabus Elements
Version 12 is structured around ten official elements with scored weights of 13/7/18/16/12/11/8/4/5/6. The risk categories below sit within that wider blueprint and should be studied alongside risk principles, investment risk, model risk, governance and ERM.
- Market Risk — the risk of losses from movements in market prices, including interest rates, equity prices, foreign exchange rates, and commodity prices.
- Credit Risk — the risk that a borrower or counterparty will fail to meet their contractual obligations, leading to financial loss.
- Operational Risk — the risk of loss from inadequate or failed internal processes, people, systems, or external events.
- Liquidity Risk — the risk that a firm cannot meet its short-term financial obligations due to an inability to convert assets into cash quickly enough.
- Regulatory Risk — the risk arising from changes in laws, regulations, or supervisory expectations that impact how financial firms operate.
Allocate study time to the official weighting. Operational risk is the largest element at 18 questions, followed by credit risk at 16, risk principles at 13 and market risk at 12.
Market Risk — What the Exam Tests
Market risk is arguably the most quantitative section of the exam. You will need to understand:
- Value at Risk (VaR): a loss threshold for a stated horizon and confidence level, not the maximum possible loss. A one-day 99% VaR of £10 million means the model expects losses to exceed £10 million on about 1% of days; it says nothing about how large those tail losses may be.
- Interest rate risk — how changes in interest rates affect the value of fixed-income instruments and banking books. Understand duration, convexity, and basis risk.
- Foreign exchange risk — the exposure firms face when operating across multiple currencies. Transaction, translation, and economic exposure are all examinable.
- Stress testing — regulators require firms to model extreme but plausible scenarios. Understand how stress tests complement VaR and why VaR alone is insufficient.
The exam frequently presents scenarios where you must choose the appropriate risk measure for a given situation, so focus on understanding when and why each tool is used — not just the definitions.
Credit Risk and Counterparty Exposure
Credit risk questions test your understanding of how financial institutions assess and manage the probability that borrowers or counterparties will default.
Key areas to master include:
- The five Cs of credit — Character, Capacity, Capital, Collateral, and Conditions. These form the foundation of credit assessment frameworks.
- Credit ratings — understand how agencies like Moody’s, S&P, and Fitch assign ratings, and the difference between investment-grade and speculative-grade debt.
- Expected Loss formula: EL = PD × LGD × EAD (Probability of Default × Loss Given Default × Exposure at Default). Keep the units consistent and remember that LGD is the loss proportion after recoveries, so a higher recovery rate lowers LGD rather than PD or EAD.
- Counterparty credit risk — particularly relevant for derivatives and repo markets. Understand netting agreements, collateral management, and central clearing.
- Credit risk mitigation — techniques such as collateralisation, guarantees, credit insurance, and credit derivatives (e.g., credit default swaps).
Scenario questions in this section often describe a lending or trading situation and ask you to identify the appropriate risk mitigation strategy.
Free CISI Risk in Financial Services Practice Questions & Exam Preview
Try 15 CISI Risk in Financial Services practice questions from Principles of Risk Management
Practice CISI Risk in Financial Services exam questions with answers and explanations. The full course includes 5 mock exams and complete syllabus coverage.
Exam Preview
A firm identifies repeated payment errors. Which sequence best supports managing the risk?
Flashcards
What is the minimum capital requirement under Basel regulations?
Focus Learn
- Definitions of risk and uncertainty
- Specific risks in financial services (credit, market, operational, liquidity)
- Systemic risk and contagion
- External vs internal drivers of risk
- Risk appetite and risk culture
- Inherent (gross) vs Residual (net) risk
- FinTech, RegTech, digital assets, blockchain, cryptocurrencies and smart contracts
- Benefits and problems associated with disruptive innovation
Every business faces risks that present threats to its success. In its broadest sense, risk is defined as the possible harm associated with a situation – the product of impact and probability. Risk management is the practice of using processes, methods and tools for quantifying and managing these risks and uncertainties. An important aspect of the financial services sector is the management of financial risk on behalf of both customers and owners. To discuss the risks faced by a financial services firm is, therefore, to address one of the core reasons for its existence. For risk management practitioners, that is what gives the disciplines within risk management their importance and their intellectual appeal.
The Bank for International Settlements (BIS) defines several specific key areas…
Unlock all Focus Learn
Open every chapter’s key areas, pitfalls, exam traps and key numbers.
Operational Risk — Beyond IT Failures
Operational risk is one of the broadest categories tested on the exam. While IT system failures are the most commonly cited example, the Basel Committee identifies seven distinct categories of operational risk events:
- Internal fraud — unauthorised trading, theft by employees, intentional mismarking of positions
- External fraud — robbery, hacking, identity theft, third-party forgery
- Employment practices — discrimination claims, health and safety violations, workers’ compensation
- Clients, products, and business practices — mis-selling, market manipulation, product defects
- Damage to physical assets — natural disasters, terrorism, vandalism
- Business disruption and system failures — hardware/software failures, telecommunication outages
- Execution, delivery, and process management — data entry errors, failed mandatory reporting, incomplete legal documentation
The exam tests whether you can correctly classify a given scenario into the right operational risk category. Pay close attention to the distinction between internal fraud (employee-driven) and external fraud (third-party-driven), as these are frequently confused.
Liquidity Risk and Basel III Requirements
Liquidity risk has become a central focus of financial regulation since the 2007–2009 financial crisis. The exam tests both conceptual understanding and knowledge of specific regulatory ratios.
Key topics include:
- Funding liquidity risk vs market liquidity risk — funding risk relates to a firm’s ability to meet its obligations as they fall due, while market liquidity risk relates to the ability to sell assets without significant price concessions.
- Liquidity Coverage Ratio (LCR) — requires banks to hold sufficient High-Quality Liquid Assets (HQLA) to cover net cash outflows over a 30-day stressed period. HQLA is divided into Level 1 (cash, central bank reserves, sovereign debt) and Level 2 assets.
- Net Stable Funding Ratio (NSFR) — a complementary measure ensuring that banks maintain a stable funding profile in relation to the composition of their assets over a one-year horizon.
- Contingency funding plans — expect questions on how firms prepare for liquidity stress events, including access to central bank facilities and pre-positioned collateral.
Questions in this section often present a scenario describing a firm’s cash flow position and ask you to determine whether the LCR threshold is being met.
Regulatory Frameworks — Basel III and Beyond
The regulatory section ties the other four risk categories together. You must understand how the Basel framework governs capital adequacy, supervisory oversight, and market transparency.
Essential knowledge includes:
- The three pillars of Basel — Pillar 1 (minimum capital requirements for credit, market, and operational risk), Pillar 2 (supervisory review process), and Pillar 3 (market discipline through disclosure).
- Capital tiers — Tier 1 capital (Common Equity Tier 1 and Additional Tier 1) versus Tier 2 capital. Know the minimum CET1 ratio of 4.5%, Tier 1 ratio of 6%, and total capital ratio of 8%.
- Capital buffers — the Capital Conservation Buffer (2.5%), Countercyclical Buffer (0–2.5%), and G-SIB surcharge for globally systemically important banks.
- Risk-weighted assets (RWA) — how different asset classes receive different risk weightings under the Standardised Approach and the Internal Ratings-Based (IRB) Approach.
- Leverage ratio — the non-risk-based backstop measure introduced to complement risk-weighted capital requirements.
Regulatory questions are often the most interconnected on the exam. A single scenario might involve credit risk (loan default), operational risk (process failure), and regulatory risk (breach of capital requirements) simultaneously. Practice identifying the primary risk category in such compound scenarios.
Building Your Study Plan for the Risk Exam
A structured study plan is useful for this Level 3 qualification. Here is a recommended 8-week timeline:
- Weeks 1–2: Cover market risk and credit risk in depth. These are the most quantitative sections and benefit from early attention.
- Weeks 3–4: Study operational risk and liquidity risk. Focus on the Basel definitions and regulatory ratios.
- Weeks 5–6: Cover regulatory frameworks and begin taking topic-level practice quizzes. Revisit weak areas identified through practice.
- Weeks 7–8: Full mock exams under timed conditions. Aim for at least three complete practice exams, scoring 75%+ before sitting the real exam.
For a broader perspective on study techniques that apply across all CISI qualifications, see our guide on how to pass your CISI exam on the first attempt. If you are also considering other CISI certifications, our Ultimate Guide to CISI Exams in 2026 provides an overview of available modules and career pathways.
Frequently Asked Questions
1 What topics does the CISI Risk in Financial Services exam cover?
Version 12 has ten syllabus elements: risk principles, international risk regulation, operational risk, credit risk, market risk, investment risk, liquidity risk, model risk, corporate governance and enterprise risk management. The scored-paper weights are 13%, 7%, 18%, 16%, 12%, 11%, 8%, 4%, 5% and 6%.
2 How difficult is the CISI Risk in Financial Services qualification?
This is a Level 3 Award. It requires candidates to distinguish interconnected risk categories and apply risk-management and regulatory principles to objective-test scenarios.
3 How long should I study for the CISI Risk in Financial Services exam?
Build the plan around your starting knowledge and the current Version 12 syllabus. Give most time to operational risk (18%), credit risk (16%), risk principles (13%) and market risk (12%), then use timed mocks to identify gaps.
4 What is the pass mark for the CISI Risk in Financial Services exam?
The official Version 12 sample paper uses a pass mark of 70 correct answers out of 100 scored questions.
5 Can I use real-world work experience to prepare for the Risk in Financial Services exam?
Yes, practical experience in banking, compliance, or risk management is highly beneficial. However, the exam tests specific frameworks, thresholds, and regulatory definitions that go beyond general awareness. Supplementing experience with targeted study materials and practice questions is essential for success.
Keep learning
Related Insights
CISI Risk in Financial Services: Top Concepts You Must Master to Pass
Master the CISI Risk in Financial Services syllabus. Learn why 40% of candidates fail, discover the hardest topics, and practice with mock exam questions.
Is CISI Risk in Financial Services Worth It? Career Guide
Assess whether the CISI Risk in Financial Services exam is worth it for risk, compliance and operations careers, including exam demands and limitations.
Best CISI Risk in Financial Services Mock Exams & Free Sample Papers (2026)
Get the best CISI Risk in Financial Services mock exams. Practice with a rich question bank, community-polished questions, and take our free sample paper.
Ready to Prepare for Your Exam?
Prepare with syllabus-aligned study tools, realistic practice and course-grounded AI support.
Explore Courses