Table of Contents
- • The Paradigm Shift: From Recovery to Resilience
- • Core Pillars of the DFSA Framework
- - 1. Identification of Critical Business Services
- - 2. Setting Impact Tolerances
- - 3. Resource Mapping and Scenario Testing
- • Interconnected Risk: Third-Party Dependency Management
- • Governance and Accountability
- • Compliance Career Path: Elevating Your Profile
- • Practise the Proposal and Rule Distinction
Explore syllabus-aligned study tools, realistic practice and course-grounded AI support.
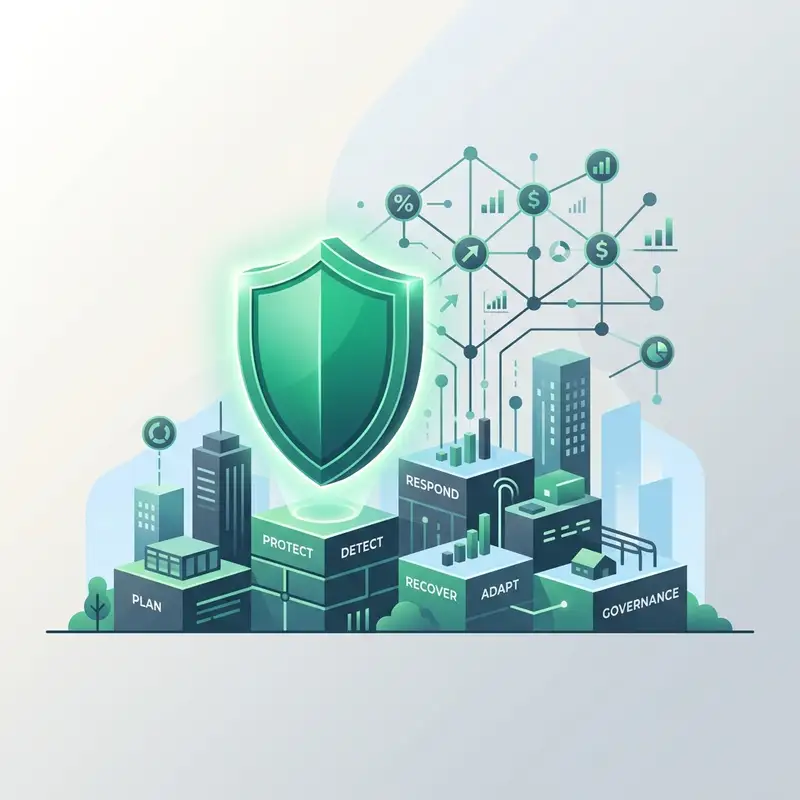
In an increasingly interconnected and digital financial services landscape, the traditional focus on financial resilience (capital and liquidity) is no longer sufficient. Regulators globally have recognized that operational failures can threaten both individual firm viability and systemic financial stability.
To address this, the Dubai Financial Services Authority (DFSA) released Consultation Paper 170 (CP170) on operational resilience on 27 March 2026, with comments due by 26 May 2026. CP170 set out proposals, not final binding rules. Compliance officers, senior managers, and candidates preparing for the CISI Global Financial Compliance (GFC) examination should use the concepts below as consultation context and check later DFSA rulebook amendments before treating them as requirements in the Dubai International Financial Centre (DIFC).
Status checked on 25 October 2026: No final CP170 instrument was identified in the official sources reviewed. The CP170 paper and draft appendices remain consultation sources. The current GEN chapter 5 and amendment notices should be checked for later changes before assigning obligations.
The Paradigm Shift: From Recovery to Resilience
Historically, firms approached operational disruptions through the lens of Business Continuity Management (BCM) and Disaster Recovery (DR). BCM and DR already plan for interruption and recovery. Current GEN 5.3.23 requires adequate arrangements to continue functioning and meet obligations after an unforeseen interruption, with arrangements kept current and regularly tested.
The model proposed in CP170 adds an explicit critical-service and harm-tolerance focus to planning for disruptions that may occur due to cyber-attacks, technological failures, third-party vendor collapses, or natural disasters. Rather than focusing solely on prevention, the proposal would expect relevant firms to maintain the delivery of critical business services during a disruption.
Core Pillars of the DFSA Framework
CP170 identified five essential elements for its proposed operational-resilience regime:
- Identify critical business services.
- Set an impact tolerance for each critical business service identified.
- Map the resources needed to deliver each service within its tolerance.
- Test the ability to remain within tolerances under severe but plausible scenarios.
- Notify the DFSA of a material disruption that breaches or comes reasonably close to breaching a tolerance.
1. Identification of Critical Business Services
Under draft GEN 5.6.2, an Authorised Person within scope would regularly assess which business services, if disrupted, could cause a material risk to users of its financial services or to the stability, reputation of, or confidence in the DIFC financial-services industry. Only a firm that identified at least one critical business service would proceed to the rest of the proposed regime. The accompanying draft GEN application text excludes Authorised ISPVs from section 5.6 and excludes Representative Offices from chapter 5; do not apply the proposal automatically to every firm.
2. Setting Impact Tolerances
For every identified critical business service, the proposal would require an Impact Tolerance. This is the maximum level of disruption beyond which the effect becomes intolerable. Paragraph 29 of CP170 discusses time or other relevant metrics, such as transaction count or value. The draft GEN 5.6.1(b), however, defines the measure as a length of time and any other relevant metrics. Read the narrative alongside that draft wording; neither supplies a universal threshold or establishes a current binding rule.
The proposed tolerance would be set at a point before intolerable harm is caused to clients or the financial system, not merely before it becomes financially inconvenient for the firm.
3. Resource Mapping and Scenario Testing
CP170 proposed that a firm map the minimum people, processes, technology, facilities and information needed to deliver each critical business service within its tolerance. The firm would then test its ability to remain within the tolerance under severe but plausible scenarios. Such tests could include:
- Multi-day power grid and telecommunication outages.
- Complete corruption of core database servers.
- Concurrent failure of primary and secondary third-party cloud service providers.
- Major ransomware attacks locking down all corporate workstations.
Interconnected Risk: Third-Party Dependency Management
A significant focus of the CP170 proposals is management of third-party risks. Modern DIFC firms rely heavily on outsourced solutions for cloud hosting, portfolio management systems, and custodial services.
Under CP170’s proposed approach, outsourcing a service would not outsource the firm’s responsibility. Relevant firms would maintain visibility over the operational resilience of material service providers through measures such as:
- Conducting detailed due diligence on vendor backup capabilities.
- Inscribing clear operational resilience and incident-reporting covenants in Service Level Agreements (SLAs).
- Integrating key third-party providers directly into the firm’s severe but plausible scenario testing.
Governance and Accountability
CP170 assigned two specific approvals to the firm’s Governing Body:
- Approve the outcome of the critical-business-services identification exercise.
- Approve the impact tolerances.
CP170 separately proposed that findings from tolerance reviews, resource mapping and scenario testing be documented and retained for internal use and possible DFSA submission. It did not call this record a Self-Assessment Document or expressly assign approval of test results to Senior Management.
Compliance Career Path: Elevating Your Profile
Operational resilience is relevant to DIFC firms and to compliance professionals who help assess service dependencies, governance and disruption testing.
Knowledge of operational resilience, complemented by professional certifications such as the CISI Global Financial Compliance (GFC), supports work on governance and risk oversight. The GFC syllabus provides broader regulatory foundations; it does not turn CP170’s consultation proposals into examinable DFSA rules.
For professionals building a compliance career in the DIFC, the practical distinction is between preventing avoidable incidents and limiting harm when disruption occurs.
Practise the Proposal and Rule Distinction
These original article exercises test the source distinctions discussed above. They are not official CISI examination questions or a statement that CP170 is part of the GFC assessment.
Free CISI Global Financial Compliance Practice Questions & Exam Preview
Try 4 CISI Global Financial Compliance practice questions from DFSA CP170 consultation and current continuity duties
Practice CISI Global Financial Compliance exam questions with answers and explanations. The full course includes 5 mock exams and chapter study tools.
Exam Preview
A compliance officer finds FINAL in the CP170 PDF filename after the consultation deadline. What should she conclude?
Flashcards
Does the CP170 consultation deadline enact rules?
Focus Learn
- Consultation status and source hierarchy
- Current continuity planning and testing duties
- Critical business services and draft scope exclusions
- Impact-tolerance narrative and draft metric wording
- Proposed Governing Body approvals and retained records
Use the current rulebook for binding duties and CP170 with its draft appendices for the proposed service-based regime. Check scope, sources and later instruments before deciding what a firm must do.
Unlock all Focus Learn
Open every chapter’s key areas, pitfalls, exam traps and key numbers.
Frequently Asked Questions
1 What is the primary objective of the DFSA Operational Resilience Framework?
CP170 proposed a framework intended to improve how relevant firms prevent, adapt to, respond to, recover from and learn from operational disruptions. CP170 is a consultation paper, so its proposals should not be cited as final rules without checking subsequent DFSA rulebook amendments.
2 Which firms are subject to the DFSA CP170 guidelines?
CP170 consulted on the proposed scope and proportional application; it was not itself an in-force guideline applying automatically to every DFSA-authorised firm. Confirm the scope in any final rulemaking and the current DFSA rulebook before assigning obligations to a firm.
3 What are critical business services under DFSA CP170?
CP170 used 'critical business service' for a service whose disruption could cause a material risk to users of the firm's financial services or to the stability, reputation of, or confidence in the DIFC financial-services industry.
4 What is an 'impact tolerance' in operational resilience?
CP170 proposed an impact tolerance for each identified critical business service: the maximum disruption beyond which the effect becomes intolerable for users or the DIFC financial-services industry. The paper discusses time or other relevant measures, including transaction count or value; the accompanying draft GEN definition uses length of time and any other relevant metrics. Read both as proposals and check any final rules.
5 How does the CISI Global Financial Compliance qualification help with DFSA regulations?
The CISI Global Financial Compliance (GFC) syllabus covers international regulation, risk and governance concepts that provide useful background. It does not replace the DFSA Rulebook or make CP170's consultation proposals binding or examinable rules.
Keep learning
Related Insights
UAE ESG and Sustainable Finance Compliance: What Finance Professionals Must Know in 2026
May 30, 2026 was the UAE climate law's default status-adjustment date. Explore ESG rules, sustainable finance frameworks and CISI syllabus relevance.
Mastering CISI Global Financial Compliance (GFC): Exam Tips & Quiz
Prepare for the CISI Global Financial Compliance (GFC) exam with this complete guide, including exam structure, key topics, and an interactive quiz.
Is CISI Global Financial Compliance Worth It? Career Guide
Is CISI Global Financial Compliance worth it? Compare its Level 3 exam, compliance career value, best-fit candidates, limits and alternatives.
Ready to Prepare for Your Exam?
Prepare with syllabus-aligned study tools, realistic practice and course-grounded AI support.
Explore Courses